
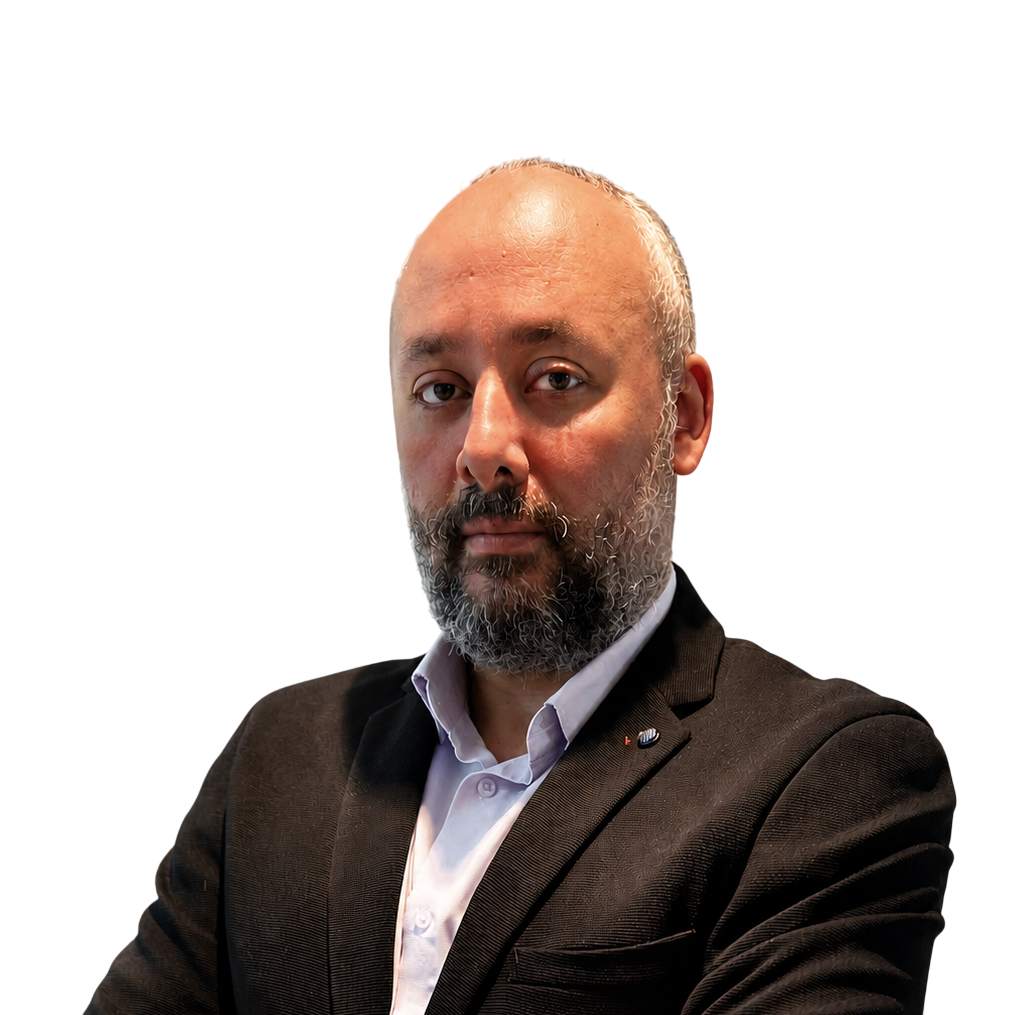
Yehia Elghaly
Lead Consultant Red Team
CPX
Yehia M. Elghaly is the Co-Founder of Defenderon and a Lead Red Team Consultant at CPX, with more than 15 years of experience in offensive cybersecurity. Throughout his career, he has conducted over 200 security assessments across government, critical infrastructure, defense, aviation, banking, energy, and telecommunications sectors. His experience includes full-spectrum red team operations and security assessments of government systems and AI-powered applications.
He holds a Master’s degree in Information Security and Digital Forensics from the University of East London. Yehia is the author of Learn Penetration Testing with Python 3.x, published in both First and Second Editions, and has discovered and responsibly disclosed more than 18 CVEs.
He is an international cybersecurity speaker and has presented at leading industry conferences, including Black Hat, DefCamp, QuBit Conference, and Null Dubai. Yehia has also authored numerous technical articles published in recognized cybersecurity magazines and industry publications, sharing his research and practical expertise in offensive security, vulnerability research, and emerging cybersecurity technologies.
Speaker sessions
Briefings and Arsenals | Confirmed Speakers | No Session Assigned
Placeholder session for confirmed speakers without an assigned session, allowing them to be pushed to Swapcard and Visit.
- 07:30
- Tue
- 01 Dec
Stage:
Briefing Stage 2
Sessions Type:
Keynote
Pwned on the Couch: Hacking Smart TVs into Surveillance Devices
Modern smart TVs expose multiple local and cloud-connected interfaces designed for convenience, including media control protocols, application lifecycle services, and browser-based user interfaces. While these components are intended to operate independently, they often rely on implicit trust assumptions that are never formally enforced.In this research, we analyze a widely deployed smart TV platform and demonstrate how these assumptions collapse when exposed to an adversarial environment. We identify a systemic trust failure that allows an unauthenticated network-adjacent attacker to interact with internal device services, influence application behavior, and execute arbitrary JavaScript within the TV�s browser context.By chaining multiple subsystems�including control interfaces, browser execution, and telemetry-related functionality�we show how low-level access can be escalated into high-impact outcomes. These include unauthorized device control, persistent UI manipulation, extraction of application-level data, and confirmed exfiltration of device and user-related information to external infrastructure.We further demonstrate real-time observation of user activity through exposed interfaces, enabling behavioral inference such as application usage patterns and interaction timing, without any user awareness.This work highlights how individually low-risk features can combine into a unified attack path when trust boundaries are not enforced across subsystems. We conclude with a discussion of architectural design flaws that enable these issues and why similar patterns are likely to exist across other smart TV ecosystems.
- 16:10
- Wed
- 02 Dec
Stage:
Briefing Stage 1
Sessions Type:
Keynote