
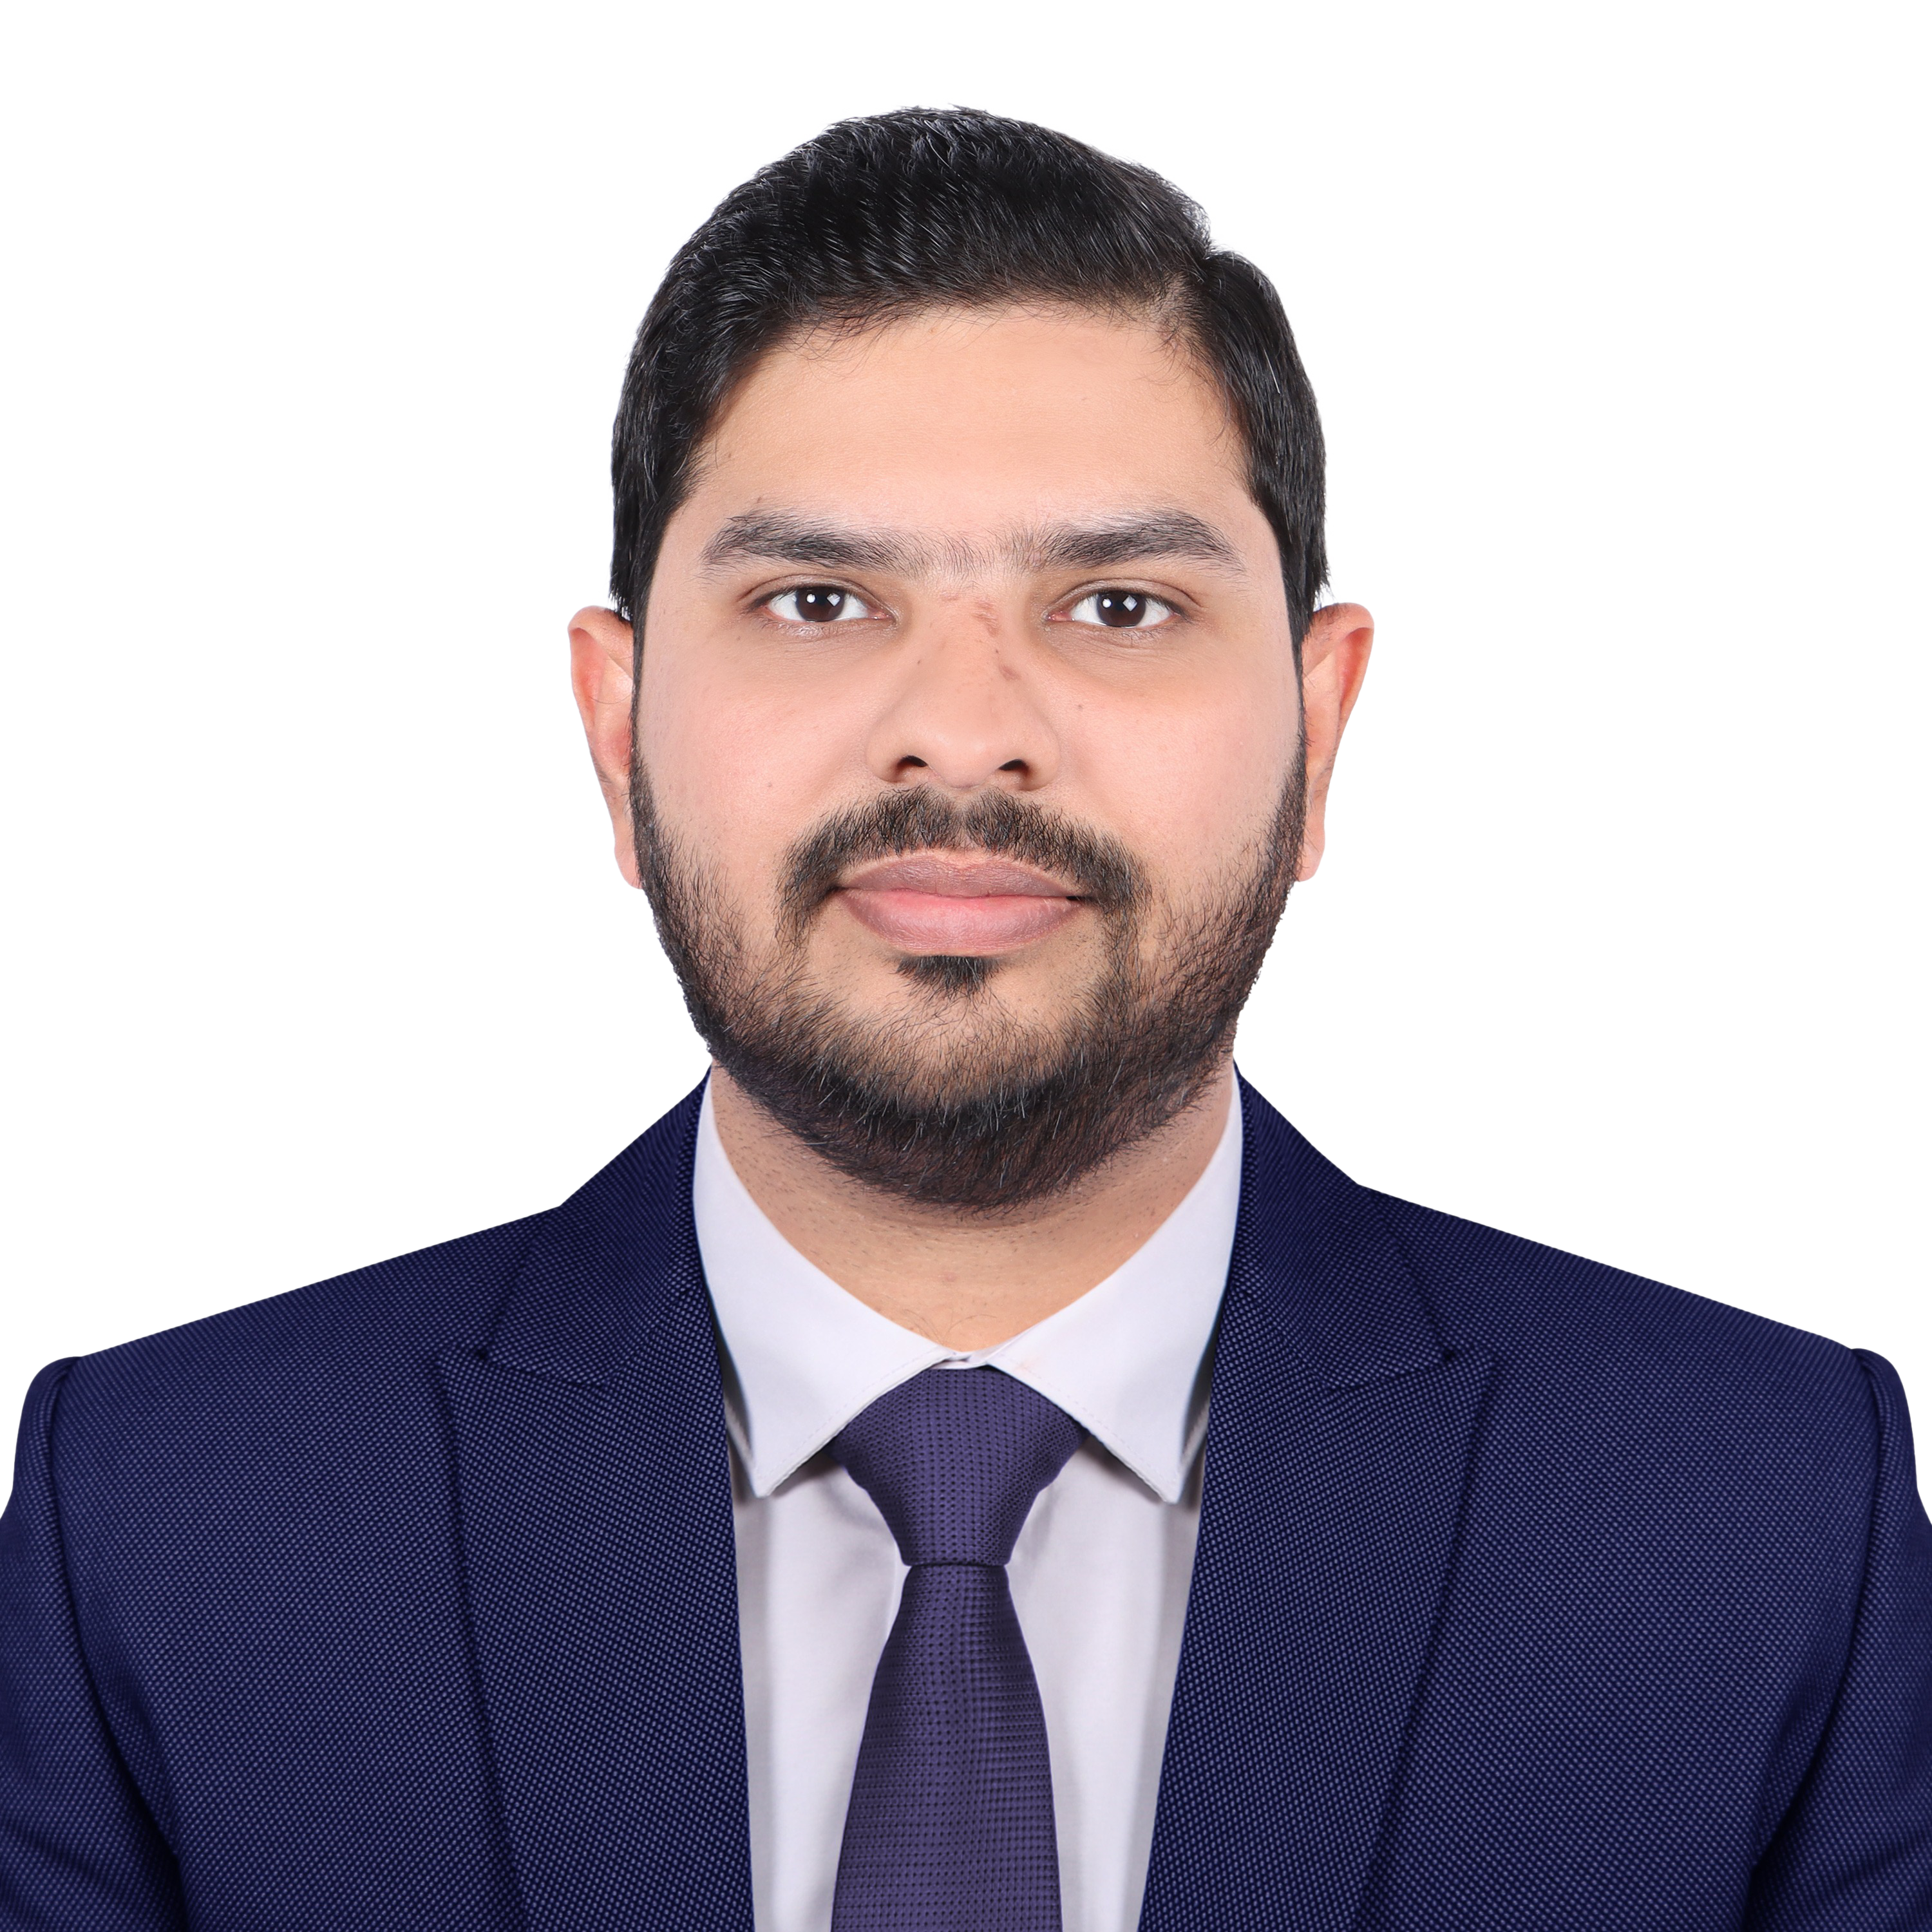
Pratik Chotalia
Security Consultant
Paramount Computer Systems LLC
Pratik Chotalia is a security consultant at Paramount Computer Systems (Dubai) with 8+ years of offensive security experience and 1,000+ penetration tests delivered across enterprise environments. He holds OSCP, OSEP, OSED, CARTP, CRTP and OffSec's AI-300 (OSAI) — the latter focused on adversarial testing of multi-agent AI systems and A2A protocols. An invite-only Synack Red Team member, he is recognized in the NASA and NCIIPC Halls of Fame. His work spans red teaming, cloud security, and emerging AI attack surfaces. He is the creator of Saarthi OPS, a local-first, AI-assisted VAPT platform that keeps target data off the cloud.
Speaker sessions
Briefings and Arsenals | Confirmed Speakers | No Session Assigned
Placeholder session for confirmed speakers without an assigned session, allowing them to be pushed to Swapcard and Visit.
- 07:30
- Tue
- 01 Dec
Stage:
Briefing Stage 2
Sessions Type:
Keynote
Saarthi OPS: AI-Driven Offensive Security That Never Leaves Your Machine
Saarthi OPS is a local-first, privacy-first, AI-assisted VAPT platform that runs an entire authorized engagement — reconnaissance through controlled attack validation — on the operator's own machine, powered by a local LLM. No target data, credentials, or evidence ever leaves the box.This Arsenal session is a live, end-to-end demonstration against a local test target. From a single authorized URL, Saarthi orchestrates reconnaissance (DNS, subdomains, live-host and HTTP intelligence, crawling, JavaScript analysis, historical-URL discovery, and local page archiving), then safe direct checks, then a bounded Phase-6 controlled-attack-validation chain: attack-hypothesis generation, a policy/approval gate, low-risk surface validators, and authenticated workflows that log in multiple accounts and replay requests across them to surface IDOR/BOLA, vertical privilege escalation, tenant-isolation breaks, and JWT/session-token weaknesses.Throughout, an AI co-pilot watches every phase live, triages findings, cross-checks them with independent tools (e.g., ghauri confirming sqlmap), and produces a ranked, evidence-backed report — all offline. Adaptive control auto-tunes scanners around WAFs and rate-limiting so scans complete without getting blocked.
The guiding principle is "autonomous yet accountable": every tool and AI action is evidence-driven, permission-gated behind a single operator authorization, scope-locked to allowed hosts, bounded, reversible, and fully audited — with secrets never persisted. Attendees see how offensive automation and AI can be both fast and trustworthy, and how to run capable AI-driven security testing without shipping client data to the cloud.
- 16:20
- Tue
- 01 Dec
Stage:
Arsenal 2
Sessions Type:
Keynote