
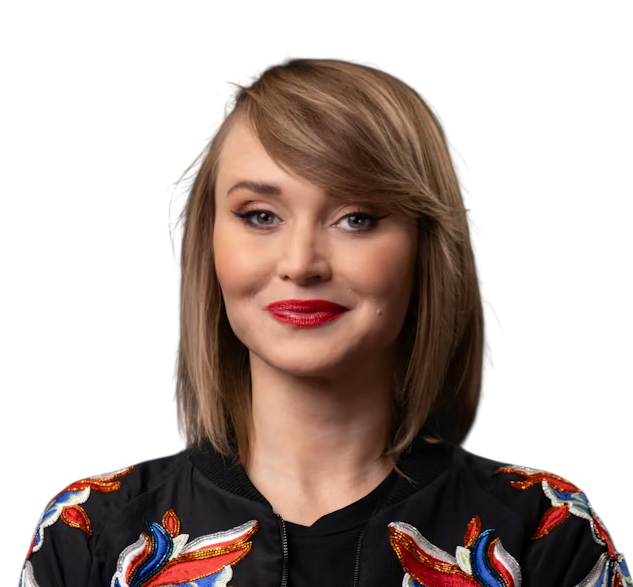
Paula Januszkiewicz
CEO and Founder, Microsoft MVP and RD
CQURE
Paula Januszkiewicz is a renowned speaker in the cybersecurity field, delivering keynotes and sessions at major global conferences. Her presentations are known for their engaging stage presence and technical depth, making her a top-rated speaker at events like Microsoft Ignite, RSA, Black Hat, and others. Paula's expertise includes penetration testing, architecture consulting, training, and seminars, with over 19 years of experience in the cybersecurity sector. She is also a Microsoft MVP and has access to the source code of Windows. Paula's keynote sessions are designed to educate audiences on the latest threats and strategies to safeguard against them.
Speaker sessions
Briefings and Arsenals | Confirmed Speakers | No Session Assigned
Placeholder session for confirmed speakers without an assigned session, allowing them to be pushed to Swapcard and Visit.
- 07:30
- Tue
- 01 Dec
Stage:
Briefing Stage 2
Sessions Type:
Keynote
CQ Automatic Destinations Toolkit: Forensics, AppID Analysis & Jump List Reverse Engineering
The CQURE Automatic Destinations Toolkit is a forensic and research-grade collection of tools designed to analyze and interpret Windows Automatic Destinations (*. automaticDestinations-ms) files, a rich but underutilized source of timeline and user activity data. These binary files, associated with Jump Lists, contain detailed historical evidence of user interaction with applications and files. The tools are used internally by the CQURE Team in advanced forensics and have been developed based on real world investigations requiring deep binary parsing and timeline construction from partially overwritten storage devices.
- 14:40
- Tue
- 01 Dec
Stage:
Arsenal 4
Sessions Type:
Keynote
CQUSNDeepAnalyzer: USN Journal Timeline Reconstruction & Behavioral Forensics Engine
CQUSNDeepAnalyzer is an advanced forensic and research-grade tool designed to analyze and reconstruct activity from the Windows NTFS Update Sequence Number (USN) Journal, one of the most valuable yet underutilized sources of low-level filesystem telemetry. While traditional tools focus on parsing raw USN records, CQUSNDeepAnalyzer goes significantly further by transforming filesystem noise into structured timelines and high-confidence behavioral insights. Developed and used internally by the CQURE Team during real-world incident response engagements, the tool enables deep reconstruction of file activity, including creation, modification, renaming, and deletion events, even in environments where artifacts have been partially removed or tampered with. It is particularly effective in detecting attacker behavior patterns such as ransomware execution, staging activity, and anti-forensics attempts. CQUSNDeepAnalyzer parses raw $UsnJrnl:$J data and builds structured timelines enriched with detection logic that identifies suspicious sequences and anomalies. The tool introduces a behavioral analysis layer on top of raw forensic data, allowing analysts to move from simple artifact parsing to understanding attacker intent and activity progression.
- 16:20
- Tue
- 01 Dec
Stage:
Arsenal 4
Sessions Type:
Keynote
Breaking Identity at Scale: From DPAPI & TBAL Secrets to Full Domain Compromise
Modern enterprise environments continue to rely on implicit trust within identity and credential protection mechanisms such as DPAPI, DPAPI-NG, and token-based authentication layers. While these technologies are designed to safeguard secrets, they also introduce powerful attack surfaces when combined with misconfigurations, weak privilege boundaries, and overlooked trust relationships.This session presents a deep technical exploration of how attackers extract and abuse protected credentials at scale, moving from local access to full domain compromise. We demonstrate novel techniques for decrypting DPAPI-protected data, abusing TBAL-related key material, and chaining these with authentication protocol weaknesses such as NTLM and Kerberos to achieve lateral movement and privilege escalation.Unlike traditional approaches that focus on single techniques, this research connects multiple layers of identity abuse into a cohesive attack path observed in real-world environments. Attendees will see how seemingly isolated weaknesses: credential storage, token handling, and protocol trust, combine into high-impact attack chains.The session also provides defensive strategies, including detection opportunities, hardening approaches, and architectural changes to reduce reliance on implicit trust. The goal is to shift defenders from reactive detection to proactive identity security design.
- 16:10
- Thu
- 03 Dec
Stage:
Briefing Stage 2
Sessions Type:
Keynote