
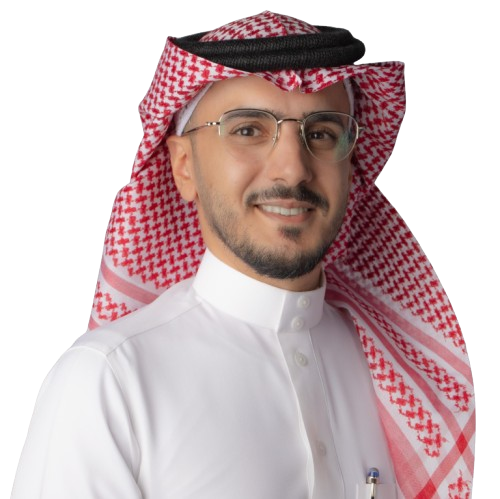
Mohammed Salami
Cyber Security Assurance Director
General Organization for Social Insurance
Mohammed is a distinguished cybersecurity researcher specializing in both offensive and defensive security, including red teaming, penetration testing, adversary emulation, and threat detection. He holds elite industry certifications underscoring his
With over a decade of experience, Mohammed has led offensive research and strengthened detection and response capabilities to secure critical systems and infrastructure, establishing himself as a trusted authority. A respected speaker, he shares insi
Passionate about advancing the field, Mohammed actively mentors emerging talent and contributes to the cybersecurity community. He frequently shares his research and insights at industry events, helping shape the next generation of security professio
Speaker sessions
Exploiting Web Push Infrastructure for Command and Control (C2)
Red teaming in Saudi government critical infrastructure begins long before the first payload lands with a regulatory problem nobody has solved publicly: how do you obtain authorization for a red team exercise when the authorization process itself undermines the exercise?Saudi Arabia's National Cybersecurity Authority requires explicit approval before any red team engages from outside the network. The requirement is sound. The process has three structural problems practitioners navigate in silence. First, the approval timeline runs one to two weeks, during which exercise dates become known in advance, eliminating the operational surprise that makes red teaming meaningful. Second, the designated submission mechanism is visible to personnel who should have no knowledge the exercise is happening, directly compromising Blue Team realism. Third, the required submission details attacker infrastructure, target dates mirror penetration testing disclosure norms, not red team operational security.This session presents two contributions. The first is a practical framework for intelligence-led red teaming in Saudi government critical infrastructure, covering team structure, four operational phases, adversary emulation versus simulation selection, and reporting standards adapted for the government sector filling the gap between SAMA's FEER framework for banking and the absence of equivalent published guidance for government entities. The second is an honest account of what the NCA authorization process looks like in practice, where it breaks for red team operations specifically, and what a compatible process would require. Both contributions are drawn from direct operational experience building and governing red team programs in Saudi government environments.
- 14:40
- Tue
- 01 Dec
Stage:
Briefing Stage 2
Sessions Type:
Keynote