
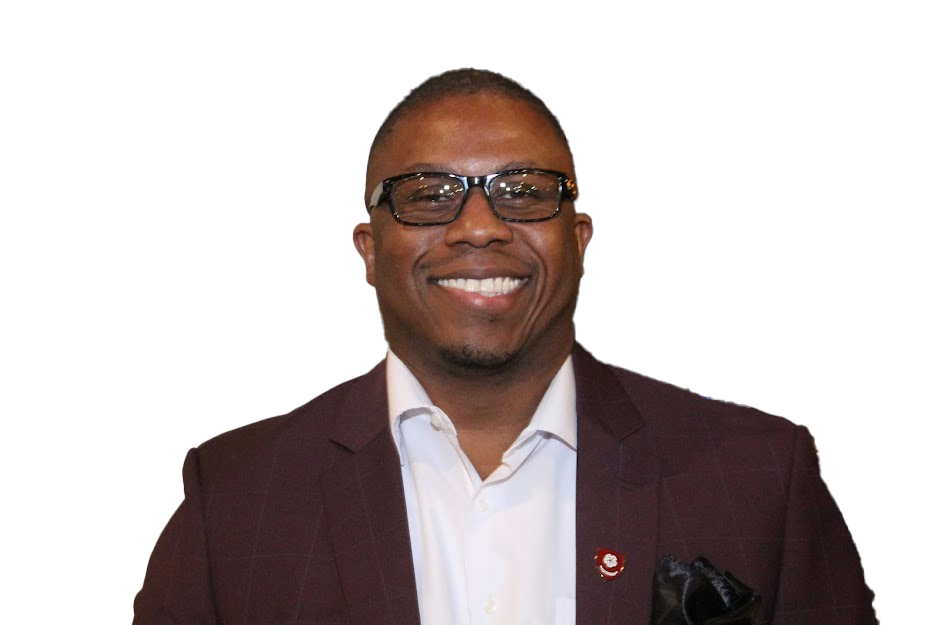
Michael Ratemo
Principal Security Advisor
Cyber Security Simplified
Michael Ratemo is a Principal Security Advisor with over 20 years of experience in cybersecurity, specializing in AI security, cloud security, threat modeling, and enterprise risk. He has presented at RSA Conference, ISACA North America Conference, ISACA GRC, and other industry events. Michael is also a LinkedIn Learning instructor whose cybersecurity and cloud security courses have reached tens of thousands of learners worldwide. He is co-author of Cloud Auditing Best Practices and holds CISSP, CCSP, CISA, and CISM certifications. His current work focuses on assessing and securing enterprise AI systems.
Speaker sessions
Briefings and Arsenals | Confirmed Speakers | No Session Assigned
Placeholder session for confirmed speakers without an assigned session, allowing them to be pushed to Swapcard and Visit.
- 07:30
- Tue
- 01 Dec
Stage:
Briefing Stage 2
Sessions Type:
Keynote
Assessing Enterprise AI Security: A Practical Methodology for Identifying AI-Specific Attack Paths
Artificial intelligence is rapidly becoming embedded within enterprise applications, yet many organizations continue to assess AI systems using traditional security methodologies that fail to identify AI-specific attack paths. As organizations deploy large language models (LLMs), retrieval-augmented generation (RAG), AI agents, external tools, and model orchestration platforms, security teams need assessment techniques that address threats beyond conventional application security testing.This session presents a structured methodology developed through practical enterprise AI security assessments and threat modeling engagements. Attendees will learn how to systematically evaluate modern AI architectures by examining trust boundaries, prompt handling, retrieval pipelines, identity and authorization models, agent capabilities, external tool integrations, data flows, and output validation.The session examines recurring security weaknesses encountered when evaluating enterprise AI systems, including prompt injection, retrieval manipulation, excessive agent privileges, insecure tool execution, insufficient authorization controls, sensitive data exposure, inadequate logging, and weak output validation.Technical demonstrations will illustrate representative AI attack paths and show how these weaknesses can be identified during security assessments.The session concludes with a practical assessment approach that security practitioners can integrate into application security reviews, penetration testing, cloud security assessments, and threat modeling exercises to identify and prioritize AI-specific risks before production deployment.
- 14:50
- Thu
- 03 Dec
Stage:
Briefing Stage 1
Sessions Type:
Keynote