
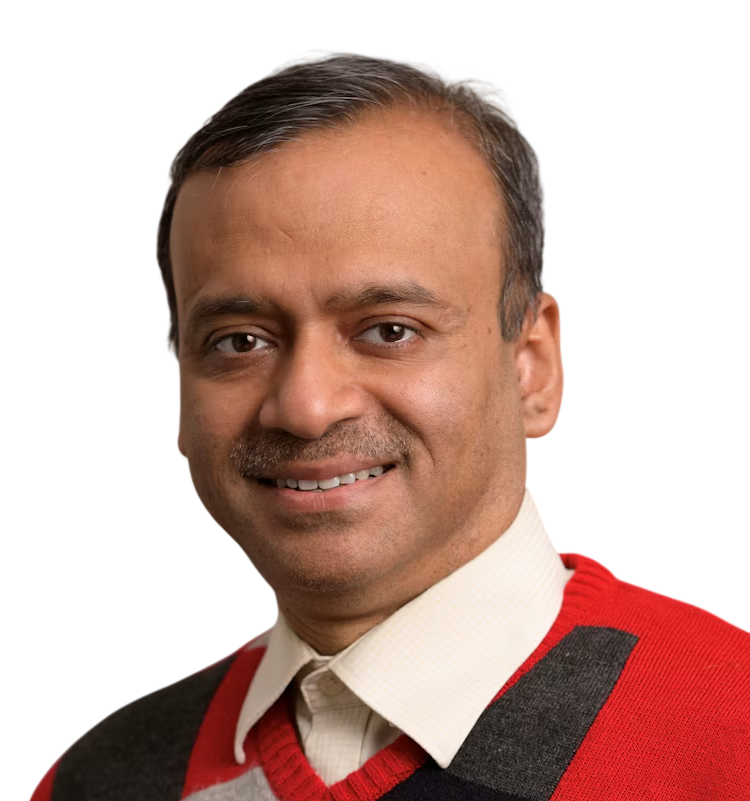
Krishnendu De
CISO
CESC Limited
Krishnendu (a.k.a KRISH or KD) is an Outcome-driven Cybersecurity Expert and hands-on Security Operation, Product Development and Engineering leader with 25+ years of progressive leadership experience securing mission-critical IT and OT infrastructure across Banking & Financial Services, Energy & Utilities, and Manufacturing sectors. Combines deep technical expertise in offensive security with ivy-league cyber security certifications (OSCP/OSEP/OSWE), cloud-native architecture, and OT/ICS protection with proven C-suite advisory, Board-level governance, and enterprise risk management capabilities. Extensive international consulting experience across 30+ countries (Europe, Middle East, Africa, Asia Pacific). Active security product developer with many open-source security tools.
Speaker sessions
Briefings and Arsenals | Confirmed Speakers | No Session Assigned
Placeholder session for confirmed speakers without an assigned session, allowing them to be pushed to Swapcard and Visit.
- 07:30
- Tue
- 01 Dec
Stage:
Briefing Stage 2
Sessions Type:
Keynote
MonitorRisk: Agentless Open-Source Security Tool for SAP S/4HANA RISE, ECS, ECC and BTP
MonitorRisk — Agentless Security Assessment for SAP S/4HANA RISE, ECC and BTP
RISE changed the deal. Customers moved their most critical business system into a shared-responsibility model where they no longer own the OS or the database — but they still own the risk, and the board still asks them to prove it. Meanwhile most SAP security tooling still assumes what RISE takes away: an agent, a privileged account, direct host access.
MonitorRisk is built for that gap. It's an agentless scanner that runs entirely outside the SAP landscape and is offline by default — point it at exports you already have, and nothing ever touches production. When you do want live data, connectors run out-of-process and strictly read-only: sapcontrol, ICF, BTP APIs, and RFC through the NetWeaver SDK. The core is Python standard library only, so there's no dependency tree to get approved before you can run it in a locked-down environment.
Today it ships 709 checks across 36 modules, and the tool understands the difference between on-premises, RISE Private Cloud, RISE Tailored and classic ECC. Findings don't stop at a list. Results feed an risk-path graph, FAIR-based risk quantification, and mappings to NIST CSF and the SAP Security Baseline, with mitigation tracked over time. A release gate mode returns clean exit codes so the same checks run in CI.
- 14:40
- Tue
- 01 Dec
Stage:
Arsenal 2
Sessions Type:
Keynote