
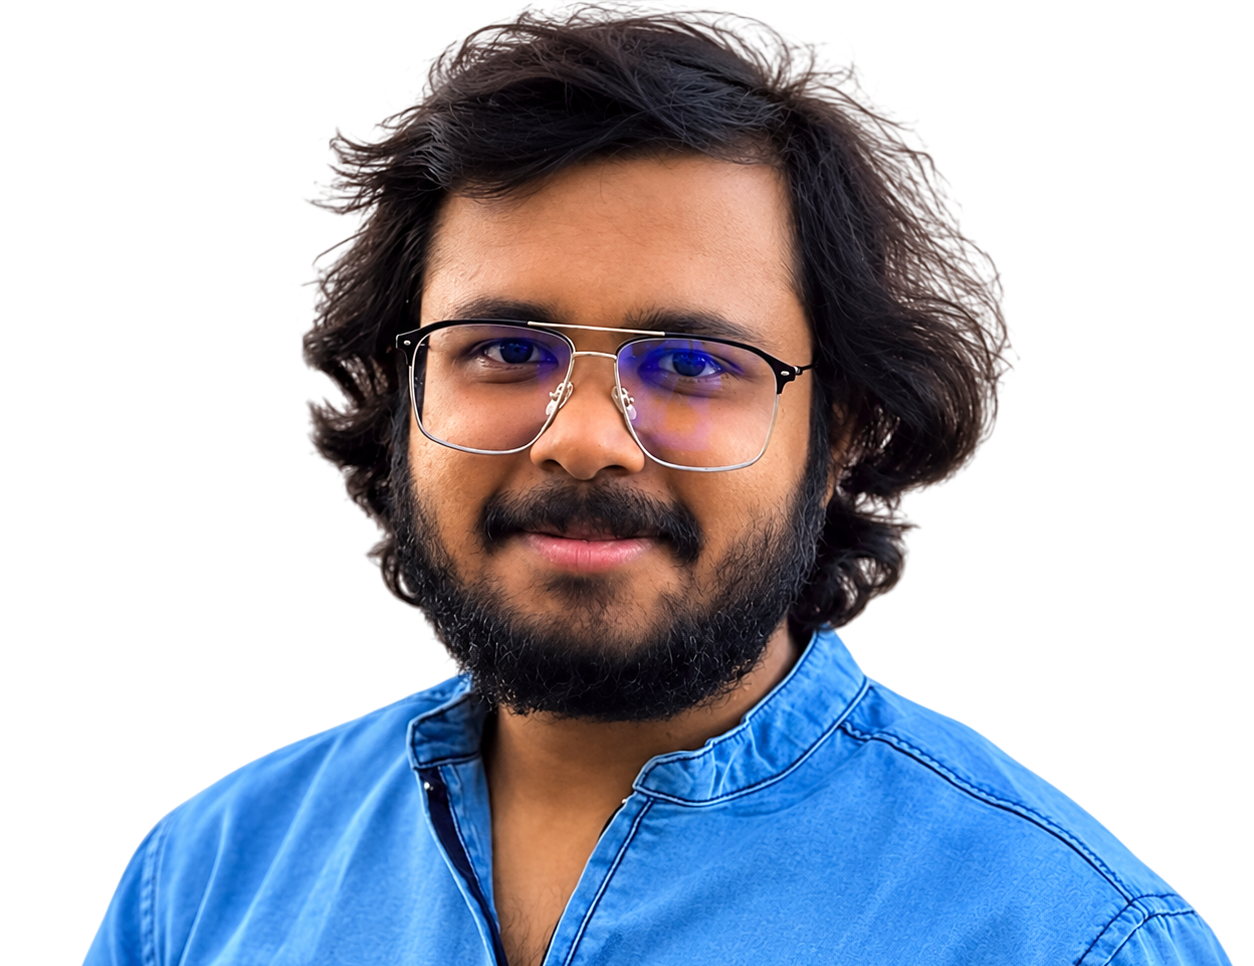
Harshit Gupta
Senior Product Security Engineer
Better World Technology Private Limited (Zeta)
Harshit Gupta (MrHAX) is a security engineer working in banking and fintech product security and a security researcher based in Bengaluru, India. His work spans offensive research, incident response, and building security tooling, with a current focus on securing AI-assisted software development. He has presented at BSides Vadodara and BSides Agra on macOS enterprise security and Gatekeeper internals and has coordinated vulnerability disclosure acknowledgements from Apple, SDKMAN, and RustDesk. He likes threat models stated honestly, controls developers do not want to disable, and secrets that never leave the laptop.
Speaker sessions
Briefings and Arsenals | Confirmed Speakers | No Session Assigned
Placeholder session for confirmed speakers without an assigned session, allowing them to be pushed to Swapcard and Visit.
- 07:30
- Tue
- 01 Dec
Stage:
Briefing Stage 2
Sessions Type:
Keynote
The Laptop Is the New Perimeter Killing Shadow-AI Exfiltration & Signing the Code That Machines Write - a local-first, zero-dependency approach
Every organisation now has two problems it cannot see. First: developers paste secrets, unreleased code, and customer data into AI tools all day, as JSON bodies inside TLS that DLP and CASB were never built to read. Second: those same tools now write a real share of the codebase, and nobody can prove which lines came from a model, under what prompt, or whether a generated block quietly carries GPL text that surfaces years later during acquisition diligence. This session argues that both problems share one root cause and one fix location: the developer's machine, the last place with full visibility. We follow a single leaked prompt from paste to provider and mark exactly where each existing control goes blind. We show why redacting secrets fails in practice: the model returns broken output, so developers switch protection off. Then we show the fix, deterministic format-preserving tokenization, which keeps the prompt working while the real value never leaves the host. We follow exfiltration into its newest channel, agent tool calls over MCP, where a simple file read can pull an API key straight into model context, and govern that stream locally. Finally, we produce signed, portable provenance for AI-written code using in-toto and DSSE, verify it live with nothing but OpenSSL, and propose the AI-code-provenance predicate type that the ecosystem is currently missing. Every demonstration runs offline with synthetic secrets. Attendees leave with techniques they can rebuild in any language. There is no product and nothing for sale.
- 17:30
- Wed
- 02 Dec
Stage:
Briefing Stage 2
Sessions Type:
Keynote