
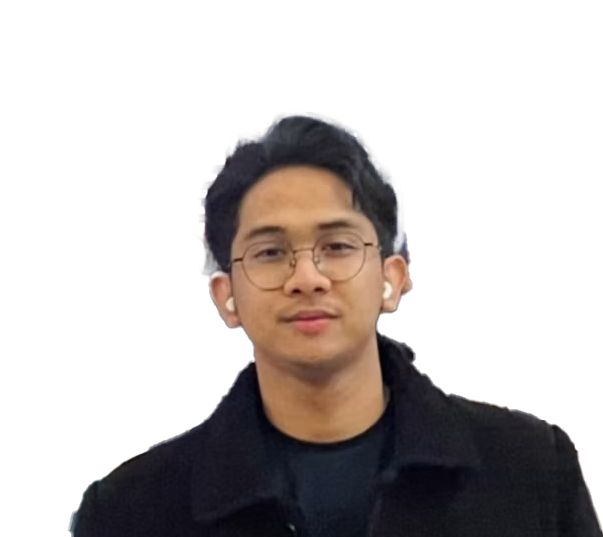
Edo Maland
Cyber Offensive Lead
softScheck APAC
Edo Maland is a senior offensive security consultant with over a decade of hands-on experience in penetration testing, adversarial simulation and red teaming. He regularly manages and leads cyber offensive teams, executing complex and unique security engagements. He is also the author of several widely used open-source tools (TheFatRat, Sudomy, etc) and developed pentesting linux distribution system from scratch (DracOs Linux)He holds multiple industry certifications in the offensive security domain, including OSCE3, OSCP+, OSWP, KLCP, and CRT(PEO), among others. He is an active speaker at cybersecurity events, including DEF CON 34, PHTALKS, and ROOTCON.
Speaker sessions
Briefings and Arsenals | Confirmed Speakers | No Session Assigned
Placeholder session for confirmed speakers without an assigned session, allowing them to be pushed to Swapcard and Visit.
- 07:30
- Tue
- 01 Dec
Stage:
Briefing Stage 2
Sessions Type:
Keynote
CodepostEx: Living off the IDE in Covert Post-Exploitation
This session focuses on the practical use of offensive tooling to demonstrate how AI-assisted code editors (AI IDEs) can be leveraged as platforms for covert post-exploitation tactics and techniques.
The tool featured in this talk is CodepostEx an open-source offensive security tool designed to target trusted AI IDE environments without requiring admin privileges and supports multiple AI IDEs
The session begins with internal recon and data collection, demonstrating how an red team operator can enumerate installed AI IDEs and trusted workspace paths, search for known vulnerabilities, extract agent interaction history, collect artifacts and file-edit history, and identify credentials or sensitive information exposed within these sources. It also demonstrates how authentication tokens can be extracted and decoded along with the decryption of locally stored extension secrets.
The focus then shifts to modern and stealthy persistence techniques within the AI IDE environment rather than relying on traditional host-level mechanisms (e.g scheduled tasks, registry run keys, or cron jobs). CodepostEx identifies trusted workspace paths and demonstrates trusted workspace poisoning a technique for achieving task-based persistence by planting malicious task configurations across trusted workspaces, mcp server injections, insecure settings manipulation that abuses trusted configurations and automation mechanisms and event-driven hooks within the AI IDE that fire on multiple event triggers such as when coding agent starts, before or after prompt is submitted, file editing and so on.
CodepostEx also generates a report that organizes collected credentials, sensitive information, conversations, and artifacts by workspace, providing operators with a centralized view for analyzing data collected.
- 14:40
- Tue
- 01 Dec
Stage:
Arsenal 3
Sessions Type:
Keynote
Your Modern AI Code Editors URI Handler Can Pop a Shell
Modern AI Code Editors are evolving from autocomplete or passive coding assistants into agentic IDE's for trusted execution environments, with built-in remote development, terminal access, and custom URI handlers. This talk explores how these features can be chained to turn a simple browser interaction into arbitrary code execution (From Browser to IDE execution)This talk will begin with a discussion of argument or command injection in SSH-based remote development workflows in AI code editors, covering both built-in or integrated. These workflows already include several security mechanisms, such as destination validation, hostname allowlisting,and directive denylist to block options that could be abused for code execution, such as ProxyCommand, LocalCommand, and KnownHostsCommand. However, during this talk, we will discuss how these mechanisms can be bypassed using alternative, undocumented, or relatively new techniques without relying on the previously blocked SSH directive. This includes techniques involving local or remote DLL loading via UNC paths and NTLM credential exposure through the IDE�s remote development workflow, providing alternative paths that can potentially bypass existing security controls.The talk will also demonstrate the complete attack chain across modern AI-powered IDEs, including Cursor, Devin and Antigravity, and discuss how similar weaknesses were identified in other editors with the focus turning URI Handlers into an RCE delivery path via argument injection bypass by demonstrating how attacker-controlled input with defense evasion techniques can be passed to trusted functions within the IDE and used to bypass existing security mechanisms.
- 13:30
- Wed
- 02 Dec
Stage:
Briefing Stage 1
Sessions Type:
Keynote