
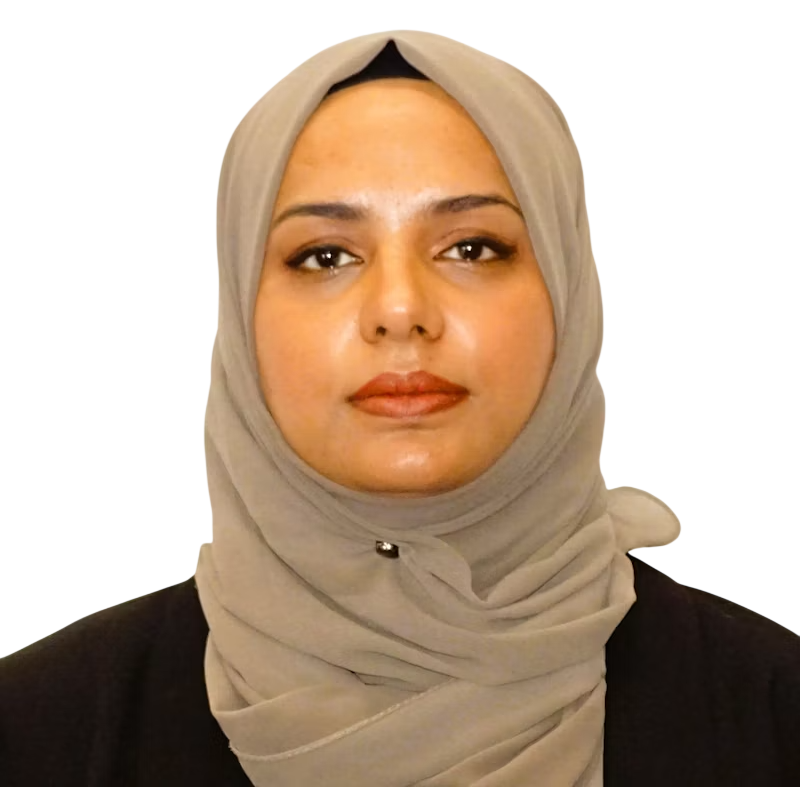
Asma Patel
Senior Lecturer in Cyber security
Aston University
Dr Asma Patel is a senior cybersecurity academic at Aston University in UK, working at the intersection of offensive security, digital forensics, and AI-driven cyber risk. With over a decade of experience, her work focuses on financial cybercrime, DeFi vulnerabilities, security operations, and cyber resilience. She has led and contributed to industry-funded projects on AI-enabled threat intelligence, attack detection, and organisational cyber defence. Dr Patel collaborates with industry and the UK government to translate research into practical security solutions. She is currently researching how adversaries exploit emerging technologies and how public and private organisations can coordinate detection, response, and mitigation.
Speaker sessions
Briefings and Arsenals | Confirmed Speakers | No Session Assigned
Placeholder session for confirmed speakers without an assigned session, allowing them to be pushed to Swapcard and Visit.
- 07:30
- Tue
- 01 Dec
Stage:
Briefing Stage 2
Sessions Type:
Keynote
AI-Enhanced Threat Intelligence Sharing for Crypto Crime and Online Harm: Privacy-Preserving Analytics and Coordinated Public-Private Response
Crypto-enabled crime and online harm are scaling faster than organisations can respond. Threat signals exist across banks, crypto exchanges, platforms, and law enforcement, but they remain siloed, delayed, and constrained by privacy and legal barriers. The result: attackers move faster than defenders.This session presents a practical, AI-driven approach to threat intelligence sharing that enables real-time detection and coordinated response, without exposing sensitive data.At the core is an �intelligence-to-action� pipeline that uses federated analytics to generate actionable intelligence locally, rather than moving raw data. Outputs are standardised using STIX and shared via TAXII, enabling interoperable, near real-time intelligence exchange across organisations. This allows defenders to correlate attack patterns across environments such as crypto transactions, fraud ecosystems, and dark-web activity.The session goes beyond detection. It shows how to operationalise intelligence into action using coordinated public-private response models. This includes decision workflows, escalation paths, and disruption mechanisms such as wallet blocking, infrastructure takedowns, and victim safeguarding.Using real-world scenarios from crypto fraud, ransomware, and online harm, the session demonstrates how adversaries exploit fragmented systems, and how defenders can close that gap with coordinated, privacy-preserving intelligence sharing.This is a practitioner-focused session for threat intelligence, DFIR, and fraud teams looking to move from fragmented detection to coordinated, real-time response.
- 16:40
- Tue
- 01 Dec
Stage:
Briefing Stage 2
Sessions Type:
Keynote