
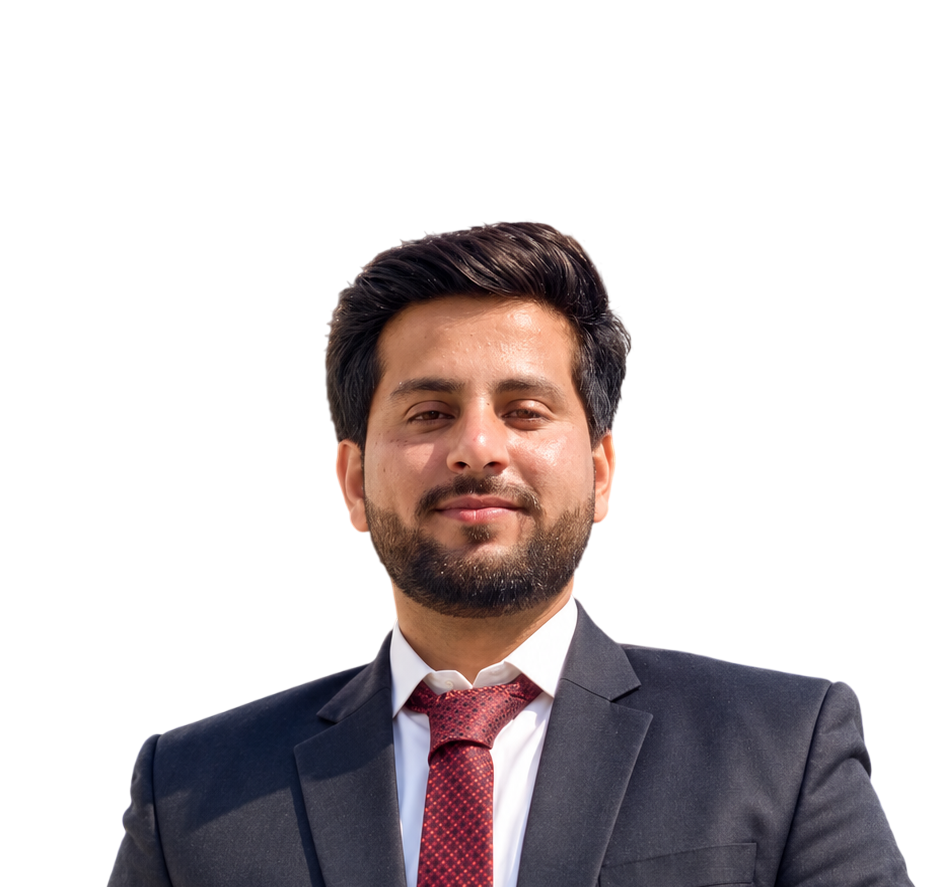
Asad Iqbal
Team Lead
REDSECLABS
Asad Iqbal is a Team Lead at RedSecLabs with over five years of experience in cybersecurity, specializing in penetration testing, red teaming, and security assessments. His work also focuses on emerging security challenges in artificial intelligence and AI-driven systems.
He has worked with organizations across the banking, financial services, healthcare, and telecommunications sectors, conducting security engagements for institutions including Alinma Bank and SAB Bank, as well as other financial organizations across Saudi Arabia, the UAE, and Bahrain.
Asad holds OSCP+, CRTP, CRTA, and MCRTA certifications and earned a Master’s degree in Information Security from NUST in 2023. He has also published peer-reviewed cybersecurity research and disclosed two CVEs through his security research.
Speaker sessions
Briefings and Arsenals | Confirmed Speakers | No Session Assigned
Placeholder session for confirmed speakers without an assigned session, allowing them to be pushed to Swapcard and Visit.
- 07:30
- Tue
- 01 Dec
Stage:
Briefing Stage 2
Sessions Type:
Keynote
Do MCP Security Gateways Actually Work? Breaking Them to Find Out
In less than a year, MCP security gateways have grown from a virtually nonexistent concept into a crowded product category. More than a dozen open-source and commercial solutions, including Obot, Lunar.dev, Microsoft�s MCP Gateway, Docker�s MCP Gateway, Kong AI Gateway, Composio, and AWS Bedrock AgentCore Gateway, now claim to protect AI agent deployments from threats such as tool poisoning, rug-pull attacks, cross-server tool shadowing, and prompt-injection-driven data exfiltration. Enterprise adoption is increasing rapidly, but independent testing has not kept pace. There is currently little publicly available research that systematically evaluates whether these products can actually prevent the attacks they claim to address.This session presents an adversarial evaluation of MCP security gateways using a fixed and reproducible set of real-world attack techniques. These include unauthenticated tool access, tool poisoning, rug-pull attacks, cross-server tool shadowing, indirect prompt injection through the �toxic triad� exfiltration chain, and SSRF-based cloud credential theft. Each gateway is deployed in front of an identical AI agent environment and tested using the same methodology. The results are presented as a reproducible pass-or-fail matrix rather than isolated or anecdotal bypasses.The session also includes a live demonstration of a complete attack chain, first against an unprotected environment and then against a representative gateway, showing where the security controls succeed or fail. Any vulnerabilities identified in commercial products will be shared with the relevant vendors through coordinated disclosure before the presentation. The goal is to help organizations move beyond marketing claims and make security decisions based on measurable, reproducible evidence.
- 12:50
- Thu
- 03 Dec
Stage:
Briefing Stage 1
Sessions Type:
Keynote