
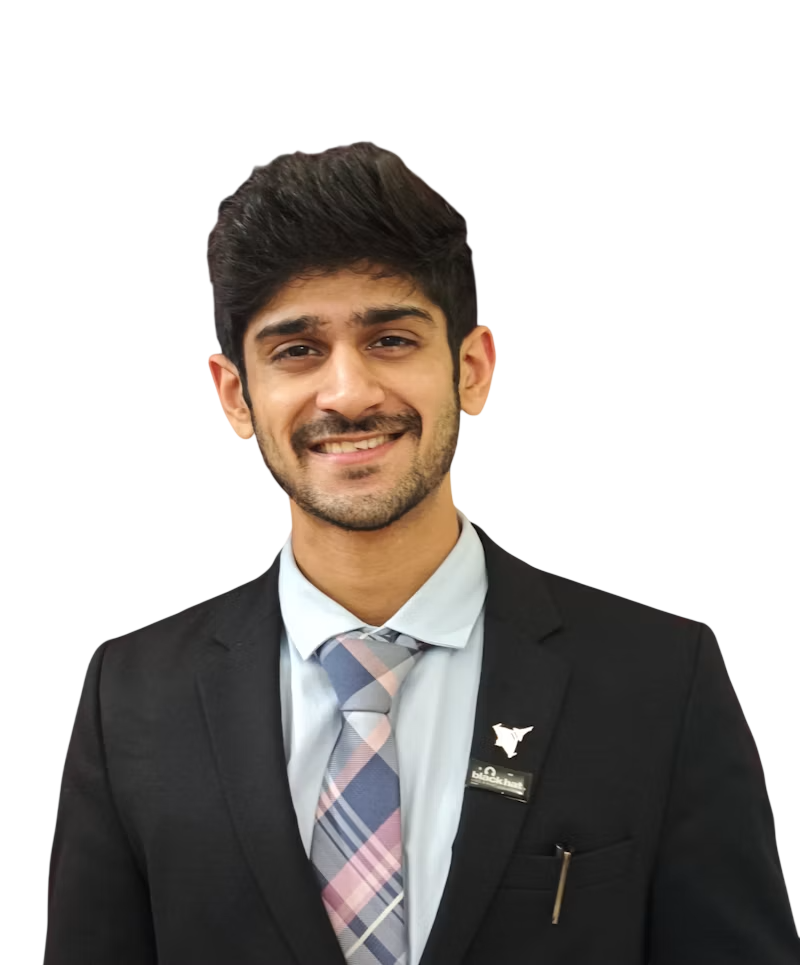
Anikait Sabharwal
Incident Responder
N/A
Anikait Sabharwal is a Cyber Security Consultant and Assistant Manager at Deloitte India, specializing in incident response, threat hunting, detection engineering, and security operations. GCIH, CySA+, and CEH certified, he is a member of the SANS GIAC Advisory Board and brings frontline experience investigating complex incidents, developing advanced detection use cases, and proactively uncovering threats. Anikait is also the co-creator of Aegis Scan, an AI-driven web vulnerability scanner presented at Black Hat MEA 2024. Beyond security operations and research, he actively mentors emerging talent and contributes to the global cybersecurity community.
Speaker sessions
Briefings and Arsenals | Confirmed Speakers | No Session Assigned
Placeholder session for confirmed speakers without an assigned session, allowing them to be pushed to Swapcard and Visit.
- 07:30
- Tue
- 01 Dec
Stage:
Briefing Stage 2
Sessions Type:
Keynote
Trusted, Tuned, Exposed: How Attackers Inherit SOC Trust
Modern SOCs continuously tune detections to manage alert volumes. Trusted accounts are allowlisted, recurring administrative activity is excluded, thresholds are raised, and frequently observed events are classified as benign. Each decision may be operationally justified, but it can also create an opportunity for adversaries to operate inside the same trusted behavior.Drawing on frontline incident response, threat hunting, and multi-environment SOC experience, this session examines real-world detection misses where attackers remained hidden not because they produced no signals, but because their activity resembled an accepted tool, identity, system, or workflow.The session discusses Adversarial Tuning Impact Assessment, a practical approach that evaluates tuning from the attacker�s perspective. Before suppressing an event, defenders assess the trust assumption behind it, determine how an adversary could exploit the same behavior, and identify the resulting loss of visibility.Rather than restoring broad and noisy alerts, the approach uses Detection Branching to create smaller, context-focused detections around meaningful deviations. Routine administrative activity may remain suppressed, for example, while focused detections examine unexpected identities, unusual assets, abnormal execution paths, changes in timing or scope, and relationships with other weak signals.Hypothesis-driven threat hunting bridges the gaps that static detections cannot fully address by converting tuning assumptions into targeted hunts for trusted-entity abuse and behavioral deviation.Through anonymized real-world examples, attendees will see what the SOC observed, why it appeared benign, how the adversary benefited, and how the tuning could have preserved both operational efficiency and investigative visibility.
- 18:00
- Tue
- 01 Dec
Stage:
Briefing Stage 2
Sessions Type:
Keynote