
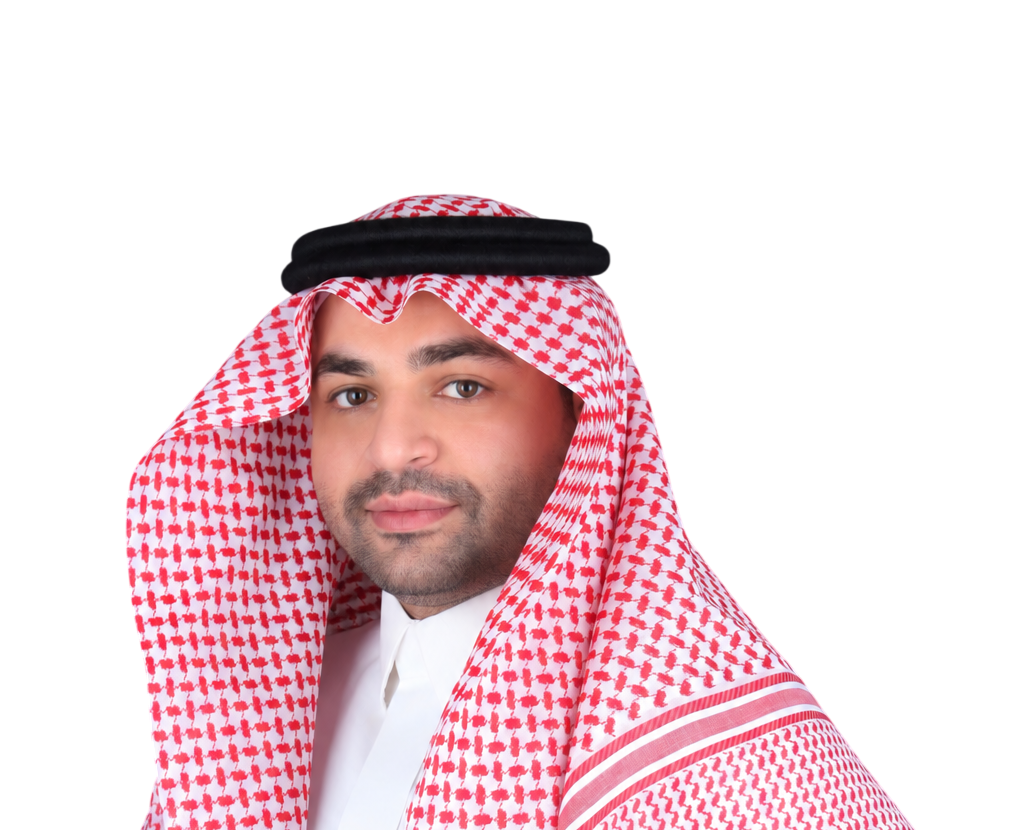
Abdullah Alenazi
SR Cybersecurity Analyst
Aramco
Senior Cybersecurity Analyst with 8+ years of experience leading enterprise vulnerability, exposure, and application security programs. Combines hands-on experties in vulnerability assessment, risk-based prioritization, security automation, threat intelligence, and application security testing with strong team leadership and operational management. Proven ability to translate technical risks into strategic decisions, improve remediation performance, and strengthen compliance with internal standards and exxternal regulatory requirements.
Speaker sessions
Briefings and Arsenals | Confirmed Speakers | No Session Assigned
Placeholder session for confirmed speakers without an assigned session, allowing them to be pushed to Swapcard and Visit.
- 07:30
- Tue
- 01 Dec
Stage:
Briefing Stage 2
Sessions Type:
Keynote
Engineering Exposure Debt for Enterprise Vulnerability Management
Enterprise vulnerability management still relies on metrics that were never designed to measure operational risk. Open vulnerability counts, SLA compliance percentages, and CVSS distributions provide useful operational statistics, but they frequently fail to answer the question security leaders actually need to understand:How much exploitable risk does the organization currently carry?This presentation introduces Exposure Debt, an engineering framework developed to measure accumulated exploitable cyber exposure rather than simply counting vulnerabilities. Traditional vulnerability metrics measure what exist; Exposure debt measures what remains exploitable, overdue, and accumulating over time. Rather than proposing another prioritization dashboard, this work presents a reproducible methodology that transforms raw vulnerability data into time-aware, exploitability-weighted risk intelligence. The framework combines CISA Known Exploited Vulnerabilities (KEV), EPSS probability scoring, vulnerability age, remediation SLA status, asset criticality, and organizational ownership into a single analytical model that identifies where enterprise risk is truly accumulating.The session introduces Exploitable Overdue Exposure Debt (EOED), a metric designed to quantify the portion of enterprise exposure that is simultaneously exploitable, overdue, and continuously increasing over time. Unlike traditional reporting, EOED measures risk accumulation rather than inventory size, allowing organizations to distinguish between healthy remediation pipelines and chronic exposure that persists despite apparently strong compliance figures.Beyond the analytical model, the presentation shares the engineering realities of implementing the framework inside a large enterprise, including data normalization challenges, vulnerability intelligence integration, ownership attribution, automation architecture, validation techniques, and production lessons learned�including a deployment defect discovered immediately before go-live that would have silently disabled organizational alerting.
- 14:10
- Wed
- 02 Dec
Stage:
Briefing Stage 1
Sessions Type:
Keynote