
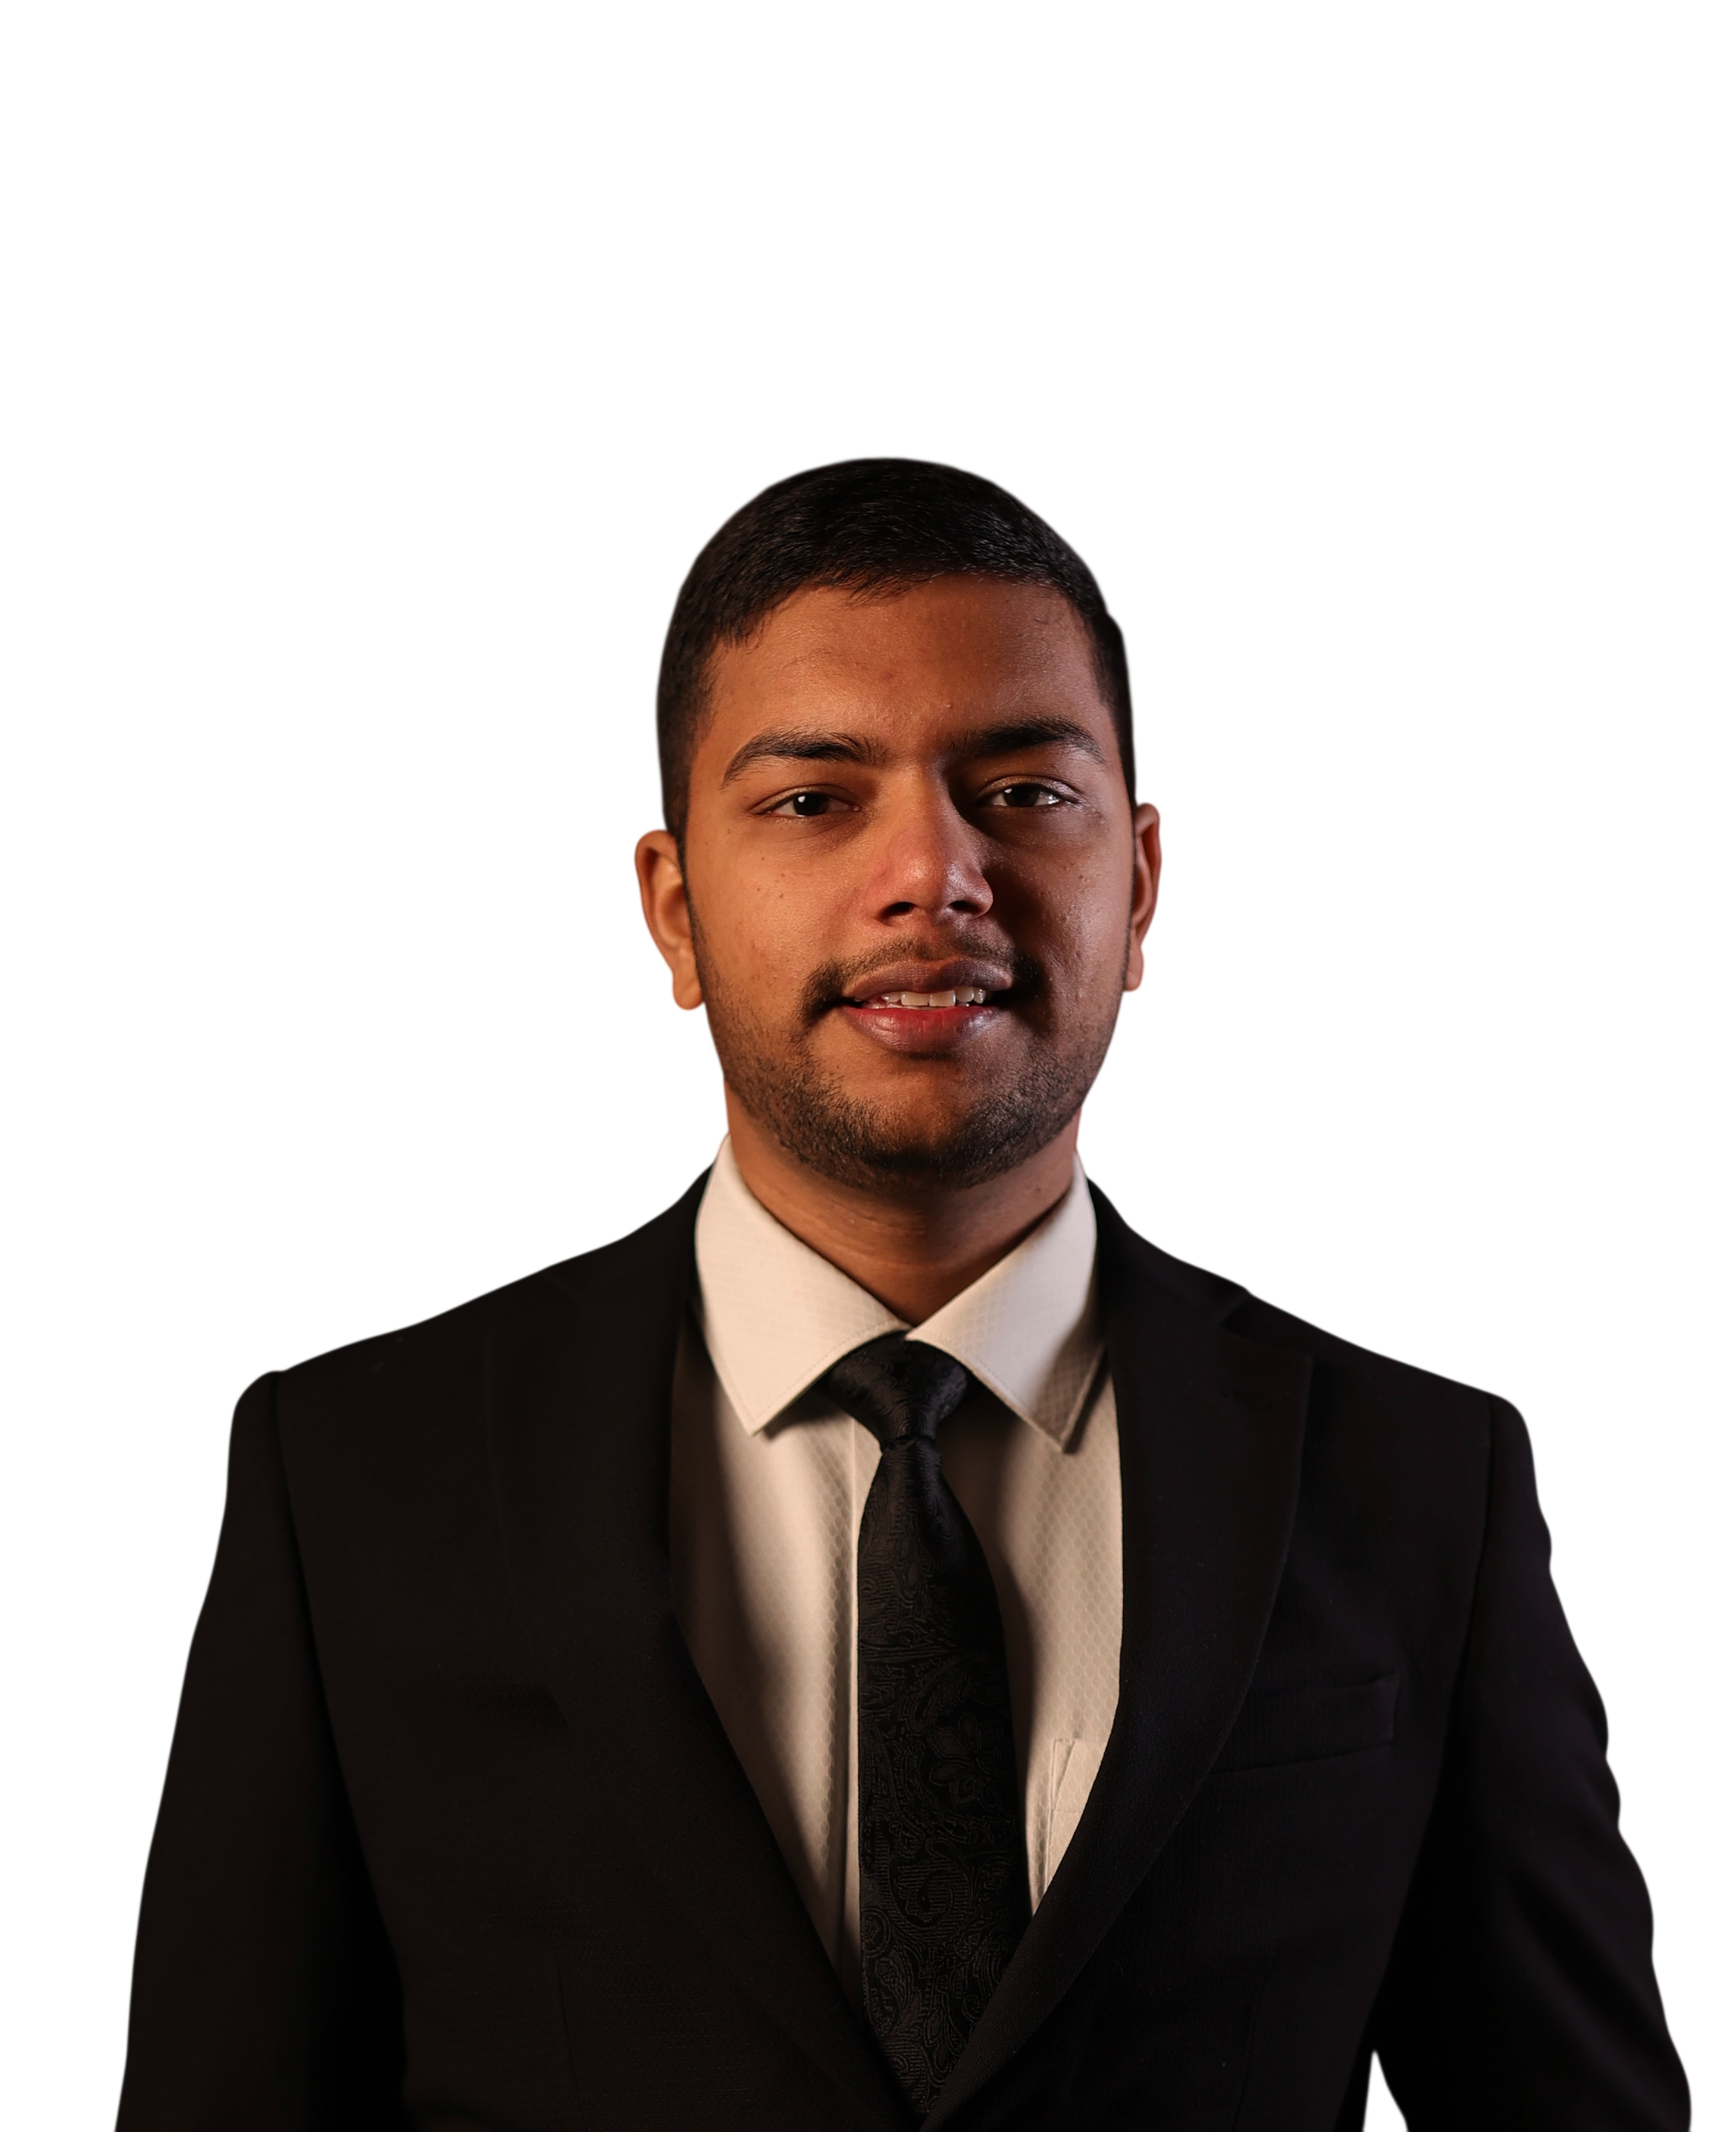
Aayush Vishnoi
Security Engineer & Research
NA
Aayush Vishnoi is a security researcher with over five years of experience in application security, specializing in API and developer surfaces exposure reconnaissance and the automation that scales it. He builds custom tooling and products that turns slow, manual security work into continuous, repeatable systems.
In 2026 he presented in the Briefings track at BSides Ahmedabad with "The AI Recon Engine," featuring his reconnaissance tool burp2model. In 2025 he presented CertMon, a tool for automated SSL/TLS certificate monitoring and vulnerability discovery, at the Seasides Goa Bug Bounty Village.
He publishes his research, tools, and security insights at falc0n.tech, driven throughout by a single aim: closing the gap between cutting edge offensive research and practical, scalable tooling that teams can actually run.
Speaker sessions
Briefings and Arsenals | Confirmed Speakers | No Session Assigned
Placeholder session for confirmed speakers without an assigned session, allowing them to be pushed to Swapcard and Visit.
- 07:30
- Tue
- 01 Dec
Stage:
Briefing Stage 2
Sessions Type:
Keynote
Plug, Play, and Prey: Exploiting the Model Context Protocol (MCP) and AI Agent Tool-Calling Infrastructure
The Model Context Protocol (MCP) is rapidly becoming the universal transport layer connecting AI agents to enterprise APIs, internal databases, and local filesystems. As developers integrate MCP tools into IDEs and autonomous agent loops, they introduce a critical, unauthenticated attack surface. This session moves past hypothetical prompt injections to analyze protocol-level exploitation. We present empirical discovery data across internet-exposed Server-Sent Events (SSE) transports, demonstrate cross-origin invocation of local developer agents via insecure CORS bindings, and detail Tool Poisoning�where malicious metadata silently coerces models into invoking privileged internal tools for data exfiltration.
- 16:40
- Tue
- 01 Dec
Stage:
Briefing Stage 1
Sessions Type:
Keynote